How the US and India Are Preparing Internet Encryption for Quantum Computers
On 27 October 2026, the US National Institute of Standards and Technology (NIST) finalised a plan to retire today's most common internet encryption methods, RSA and elliptic-curve cryptography, because future quantum computers could break them. They will be deprecated after 2030 and disallowed under NIST standards after 2035. For ordinary people nothing changes overnight, but banks, apps and governments are starting a multi-year switch to "post-quantum" encryption, and India has its own roadmap.
Last updated: 12 November 2026. Policies and deadlines in this area are still being developed and can change.
Key Takeaways
- NIST published the final version of its transition report, called IR 8547, on 27 October 2026, almost two years after the draft.
- The general timeline is two steps: quantum-vulnerable public-key methods are deprecated after 2030 and disallowed after 2035.
- US federal agencies have tighter deadlines for their most sensitive systems: 31 December 2030 for new key exchange and 31 December 2031 for digital signatures.
- The main near-term risk is "harvest now, decrypt later": attackers can store scrambled data today and unlock it once quantum computers are strong enough.
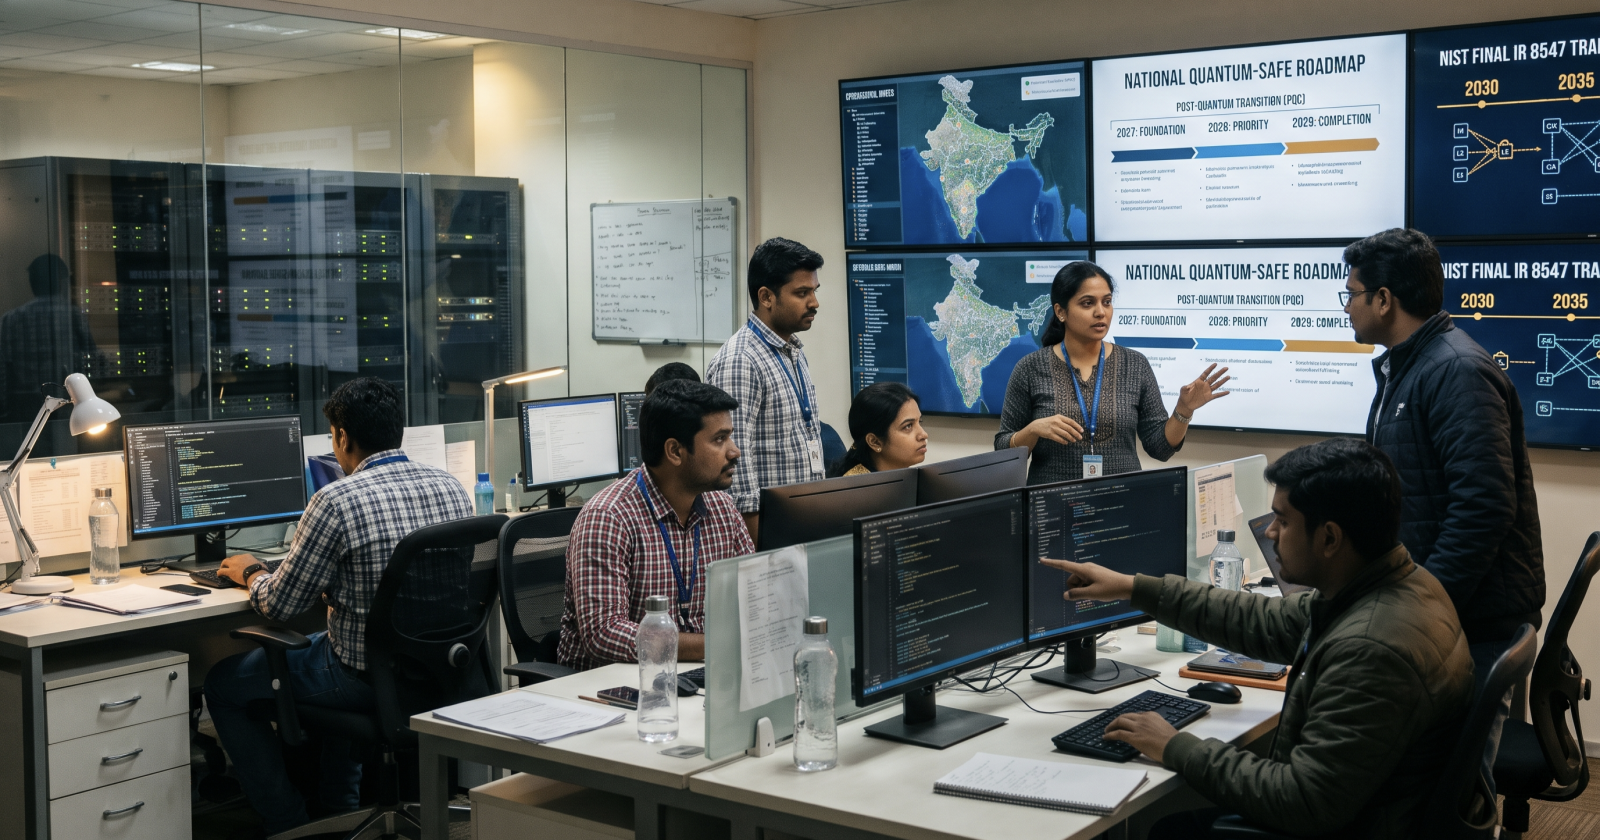
- India's quantum-safe roadmap recommends that critical sectors build foundations by 2027, move priority systems by 2028 and finish by 2029. Analysts say regulators had not yet issued binding orders.
The Problem in Plain Language
Almost everything you do online is protected by public-key cryptography: banking apps, messaging, shopping, software updates and digital signatures. Methods such as RSA and elliptic-curve cryptography rely on maths problems that ordinary computers cannot solve in a practical time.
A large enough quantum computer could solve those problems far faster. No one can say for certain when such a machine will exist, and experts disagree on the date. The reason for acting now is different: moving a large organisation to new encryption takes years, and some data must stay secret for a long time.
Harvest Now, Decrypt Later
An attacker does not need a quantum computer today to benefit from one later. Encrypted traffic copied now can be stored and read once the technology arrives. This risk is why key exchange, the step that sets up a secure connection, is the first thing to protect.
A simple, hypothetical example shows the timing problem. If a system needs five years to migrate and its data must stay private for ten years, protection has to last 15 years. Starting in 2026, that means data stays safe only if the new encryption works until about 2041. The numbers are illustrative, not a forecast.
The Key Dates
| Date | What happens |
|---|---|
| 13 August 2024 | NIST finalises its first three post-quantum standards (ML-KEM, ML-DSA and SLH-DSA). |
| June 2026 | A US executive order and an OMB memorandum (24 June) direct federal agencies to plan their migration. |
| 27 October 2026 | NIST publishes the final transition report, IR 8547. |
| 31 December 2030 | US high-value federal systems must use post-quantum key establishment. General deprecation of RSA and elliptic-curve methods begins after 2030. |
| 31 December 2031 | The same systems must use post-quantum digital signatures. |
| After 2035 | Quantum-vulnerable methods are disallowed under NIST standards and guidelines. |
From the final report, the "deprecated" label covers these methods at every approved key size, not only the weaker ones. Our arithmetic: the general deadline for removal is nine years away from 2026, and the stricter federal key-exchange deadline is four years away.
India's Position
India's Department of Science and Technology published a task force report on a quantum-safe ecosystem in 2026. It recommends a phased plan:
- Critical sectors such as banking, telecom, power and defence: foundations by 2027, priority migration by 2028, completion by 2029.
- Wider enterprises: completion by around 2033.
- Testing and certification labs: planned to be operational by December 2026.
The report also asks financial and telecom regulators to issue sector-specific guidance. According to published analysis, the Reserve Bank of India set up an expert committee called Q-SAFE in May 2026 to study the sector's readiness. As of the latest reports we found, these are recommendations, not binding orders. Readers should watch for formal regulator directions.
Who Is Doing What
| Region | Main approach | Status |
|---|---|---|
| United States | NIST standards; federal deadlines of 2030 and 2031 for sensitive systems | Binding for federal agencies; contractor rules still being drafted |
| India | Phased national roadmap, 2027 to 2029 for critical sectors | Recommended; regulator mandates awaited |
What You Can Do
Individuals cannot switch their bank to new encryption, but a few habits help.
- Keep apps, browsers and phones updated. Providers will add post-quantum protection through ordinary updates.
- Use services that explain their plans. Banks and messaging apps that publish a migration plan are taking the issue seriously.
- Think about long-lived secrets. Records that must stay private for decades, such as health or legal files, matter most.
- Do not fall for "quantum" scams. No customer needs to pay to "upgrade" their account. See our guide to staying safe from UPI scams and digital arrest fraud.
What to Watch Next
- US contractor rule: a proposed federal acquisition rule on contractor compliance is due around December 2026.
- RBI roadmap: the Reserve Bank's Q-SAFE work, and any direction to banks.
- New standards: NIST is still developing further algorithms, so the list of approved methods may grow.
- Schedule changes: NIST says it will monitor developments and adjust its transition efforts if needed.
The Factora Take
This is a quiet story with big stakes. The deadline is years away, but the work of finding and replacing old encryption is slow, and hidden systems are the hardest part. The sensible reading is not panic, since no one knows exactly when quantum machines will arrive, but preparation. Governments are setting dates, and companies that serve them will follow. Treat it like a long building project: the earlier the planning starts, the less disruptive the finish.
Frequently Asked Questions
Can quantum computers break encryption today?
The concern is about future machines. The official plans are built around preparing before a large-scale quantum computer exists, not around an attack that has already happened.
What is post-quantum cryptography?
It is a new generation of encryption and digital-signature methods designed to stay secure even against powerful quantum computers. NIST has already finalised its first three standards.
What is "harvest now, decrypt later"?
It is the idea that attackers can copy encrypted data today and read it later, when quantum computers become strong enough.
Does this affect my bank or UPI payments today?
Not directly today. Banks and payment systems are expected to migrate over the coming years, and Indian regulators are still developing sector guidance.
Does India have a deadline?
India has a recommended roadmap from its Department of Science and Technology, aiming for 2029 for critical sectors. Reports so far describe it as guidance rather than a binding national order.
Related articles